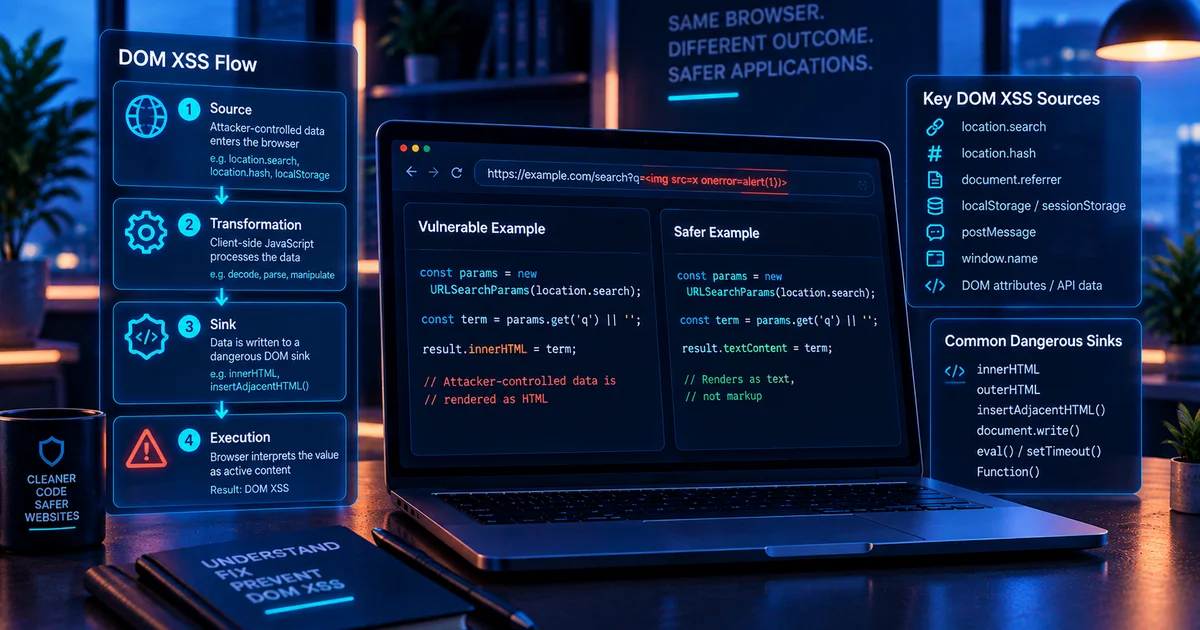
DOM-based cross-site scripting, usually shortened to DOM XSS, is one of the easiest XSS variants to misunderstand because the vulnerable behavior can exist almost entirely inside the browser. A server can return the same HTML to every visitor while client-side JavaScript reads attacker-controlled data from a URL, browser storage, a message event, or another source and then inserts that value into a dangerous DOM sink. If the value reaches an execution-capable context without the right protection, the browser can interpret attacker-controlled content as active markup or script.
For website owners and developers, the important lesson is that DOM XSS is not simply a server-side input-validation problem. The data flow must be understood inside the browser. That means identifying where untrusted data enters the page, how JavaScript transforms it, and where the value is finally written. A useful review follows the entire path instead of testing a few popular payloads and assuming failure means safety.
This guide explains the source-to-sink model, practical detection, safe remediation, retesting, framework considerations, and how external website scanning fits into a wider DOM XSS workflow. The examples are intentionally non-destructive and are intended for systems you own or are authorized to test.
What is DOM XSS?
DOM XSS occurs when client-side JavaScript processes attacker-controlled data and writes it into a browser context that can execute script or create active markup. Unlike classic reflected XSS, the vulnerable value does not always need to be embedded in the HTTP response by the server. The problem may appear only after the page has loaded and JavaScript has modified the Document Object Model.
A useful mental model is source to transformation to sink. A source is where data enters client-side code. A sink is where the application uses that data. The vulnerability appears when attacker-controlled data reaches an unsafe sink in a dangerous context without appropriate encoding, sanitization, validation, or a safer browser API.
This distinction matters when debugging. If a query parameter is safely encoded in the server response but client-side code later decodes it and assigns it to innerHTML, the vulnerability is still real. Looking only at View Source can miss the final browser behavior.
Common DOM XSS sources
location.search, which exposes query-string data to JavaScript.location.hash, which exposes the URL fragment and is not sent to the web server in the normal HTTP request.document.referrer, which may contain an attacker-influenced referring URL.window.name, which can retain values across navigations in some workflows.postMessageevent data when origins and message contents are not validated.localStorageandsessionStoragewhen attacker-controlled values can be introduced and later rendered.- DOM attributes, data attributes, hidden fields, or API response values that another untrusted source can influence.
None of these APIs is automatically vulnerable. The risk depends on what happens next. Reading location.search and writing the value with textContent is fundamentally different from assigning the same value to innerHTML.
Dangerous sinks worth reviewing
Security reviews should focus on sinks that cause the browser to parse or execute content. Common examples include innerHTML, outerHTML, insertAdjacentHTML(), document.write(), string-based code execution, and framework escape hatches that deliberately render raw HTML.
Context matters. An application may need to set an element URL, build a style, or render limited formatting. The safest design is to avoid converting untrusted strings into executable browser syntax. When HTML is genuinely required, use a maintained sanitizer with a deliberately narrow allowlist and keep the trust boundary explicit.
Safe and unsafe DOM handling
Consider a search page that displays the query term. This version asks the browser to parse the value as HTML:
const params = new URLSearchParams(location.search);
const term = params.get('q') || '';
result.innerHTML = term;
A safer version treats the value as text:
const params = new URLSearchParams(location.search);
const term = params.get('q') || '';
result.textContent = term;
The second example is safer because textContent creates text rather than markup. It does not depend on filtering specific tags, event handlers, or character combinations. This is usually more robust than trying to maintain a growing blacklist of dangerous strings.
How to test for DOM XSS safely
Step 1: Map client-side inputs
List query parameters, fragments, message listeners, route parameters, storage reads, DOM attributes, and API values that influence rendering. Browser developer tools can help you search loaded JavaScript for calls involving location, storage, postMessage, and DOM writing APIs.
Step 2: Use a unique marker before an execution test
Supply a harmless marker such as DOMXSS_TEST_84721. Search for the marker in the raw response, rendered DOM, JavaScript variables, and debugger. The purpose is to establish the data path before attempting any proof of script execution.
Step 3: Identify the sink and context
Determine whether the value reaches a text node, HTML parser, attribute, URL, JavaScript string, or framework raw-rendering API. The sink tells you which defense is appropriate. One encoding strategy does not fit every browser context.
Step 4: Prove execution minimally
If an authorized assessment requires proof, use the least disruptive demonstration possible. Avoid attempts to collect cookies, modify accounts, persist data, or send information to third-party infrastructure. The objective is to establish that attacker-controlled script execution is possible, then stop.
Step 5: Record the complete data flow
A useful finding identifies the source, transformations, sink, affected route, authentication state, victim role, and browser behavior. This is far more actionable than a report that simply states that XSS exists.
Hypothetical scenario: a client-side search widget
Imagine a documentation website that loads a static HTML shell and performs filtering entirely in JavaScript. The search term is read from location.hash so users can bookmark searches. A developer writes the term into a status banner with innerHTML because the interface originally needed a bold label.
An attacker shares a crafted link with a staff member. The web server receives a normal request because the fragment is not sent in the standard HTTP request. After the page loads, JavaScript reads the fragment and inserts it into the banner. The vulnerable behavior therefore exists only in the browser-side data flow.
A weak fix would block a handful of angle brackets or known tags. A stronger fix removes the need for HTML parsing and uses text rendering. If controlled formatting is actually required, the application can build the formatting elements itself or sanitize a narrowly defined HTML subset before rendering.
The retest should confirm that the original link no longer creates executable content, that normal search behavior still works, and that any other component using the same helper function is also safe.
DOM XSS in single-page applications
Single-page applications increase the amount of routing, state management, and rendering that happens in the browser. That does not automatically make them less secure, but it creates more browser-side data flows worth reviewing. Route parameters, API responses, cross-window messages, cached state, and persisted storage can all reach components long after the initial document has loaded.
Modern frameworks normally escape interpolated text. Risk often returns when developers bypass those protections with raw HTML rendering, direct DOM manipulation, custom directives, unsafe URL construction, or third-party widgets. A code review should therefore search for the framework's escape hatches as well as ordinary browser sinks.
postMessage deserves special attention
window.postMessage() is designed for cross-window communication and is widely used in embedded applications, payment integrations, authentication flows, and widgets. The receiving page should validate the message origin and validate the data before using it.
A receiver that accepts messages from any origin and writes message data into raw HTML can create a powerful DOM XSS path. The fix is not just output handling. The application should also restrict which origins are trusted and reject unexpected message structures.
Trusted Types and CSP as defense in depth
Large client-side applications can consider Trusted Types as an additional control around sensitive DOM sinks. Trusted Types does not replace secure rendering, but it can make accidental assignments to dangerous sinks harder by requiring values to pass through approved policies.
Content Security Policy can also reduce the impact of some XSS paths by restricting script execution. A strong policy is valuable, but it should not be mistaken for remediation. If attacker-controlled content can still reach innerHTML, the unsafe sink remains even when one payload is blocked by CSP.
Vulnify's CSP Checker can help review the policy delivered by the public website. The Security Headers Analyzer provides wider header context.
How to remediate DOM XSS
- Prefer safe sinks such as
textContentfor untrusted text. - Create elements and attributes with DOM APIs rather than concatenating HTML strings.
- Sanitize genuinely necessary user-controlled HTML with a maintained, allowlist-based sanitizer.
- Avoid string-to-code execution with attacker-influenced data.
- Validate
postMessageorigins and message structure. - Treat browser storage as untrusted if an attacker can influence its contents.
- Review framework raw-HTML APIs and trust-bypass calls.
- Add regression tests that exercise the original source-to-sink path.
How Vulnify fits into DOM XSS testing
Vulnify can support public-surface assessment by helping identify XSS-related behavior and other exposed website weaknesses during authorized testing. The XSS Payload List provides defensive test strings organized by context, while the Website Vulnerability Scanner provides a focused public vulnerability check. For broader coverage, the Website Security Scanner assesses XSS alongside other public website risks.
No external scanner can guarantee visibility into every browser state, authenticated workflow, or framework-specific trust decision. Complex DOM XSS often benefits from a combination of automated discovery, browser-based testing, code review, and manual validation.
How to verify the fix
Retest with the exact source and sink that originally demonstrated the issue. Do not conclude that the vulnerability is fixed simply because one proof string no longer executes. Inspect the new rendered DOM and confirm that the unsafe sink has been removed, constrained, or protected by an appropriate sanitizer.
Then test sibling code paths. Shared rendering helpers can appear in search results, notifications, profile previews, admin panels, and mobile web views. A fix in one component may leave the same unsafe helper active elsewhere.
DOM XSS review checklist
- Inventory URL, fragment, message, referrer, API, and storage inputs.
- Search for unsafe sinks and raw HTML rendering APIs.
- Trace untrusted values from source to sink.
- Identify the exact rendering context before choosing a fix.
- Replace HTML parsing with text rendering where possible.
- Sanitize only where raw HTML is genuinely required.
- Review CSP and Trusted Types as additional controls.
- Retest the original path after remediation.
- Check sibling components and shared helper functions.
- Add a regression test so the unsafe path does not return.
Frequently asked questions
Does DOM XSS require a vulnerable server response?
No. A static server response can still contain DOM XSS if client-side JavaScript later reads attacker-controlled data and writes it into an unsafe browser sink.
Does CSP fix DOM XSS?
No. CSP can reduce exploitability, but the unsafe source-to-sink path should still be corrected in application code.
Can an automated scanner find every DOM XSS issue?
No scanner can guarantee complete DOM XSS coverage. Dynamic state, authentication, custom JavaScript, message flows, and browser-only behavior can require manual validation or code review.
Is input validation enough?
Input validation is useful for enforcing business rules, but XSS prevention depends heavily on safe output handling. A legitimate value in one context can still be dangerous if it is inserted into an executable context incorrectly.
Conclusion
DOM XSS is best understood as a browser-side data-flow problem. Find the source, trace the value, identify the sink, and fix the context rather than relying on broad character blocking. Safe DOM APIs, narrow sanitization, secure framework defaults, CSP, Trusted Types, and regression testing create a much stronger defense. External scanning can help surface risky behavior, but reliable remediation comes from understanding the exact client-side path that allowed untrusted data to become active content.