 News
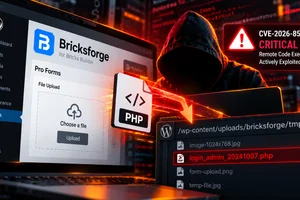
Security Brief: CVE-2026-85097 Bricksforge WordPress RCE Actively Exploited
CVE-2026-85097 is a critical unauthenticated arbitrary file upload vulnerability in Bricksforge for WordPress through version 3.1.8.9. Attackers are actively exploiting the flaw to place executable PHP files on vulnerable sites and achieve remote code execution.