 Tutorials
How to Audit Redirect Chains After a Domain or HTTPS Migration
Learn how to audit redirect chains after a domain, CDN, hosting, or HTTPS migration, find unnecessary hops and insecure transitions, and document a clean redirect baseline.
Expert articles on web security, vulnerabilities, and best practices
TutorialsLearn how to audit redirect chains after a domain, CDN, hosting, or HTTPS migration, find unnecessary hops and insecure transitions, and document a clean redirect baseline.
 Tutorials
Learn how to roll out HSTS safely using staged max-age values, includeSubDomains planning, preload requirements, certificate checks, and a practical rollback strategy.
 News
CVE-2026-8457 is a critical authentication bypass in the WooCommerce - Social Login plugin for WordPress through version 2.8.7. The Apple login handler decodes identity-token claims without verifying the JWT signature or key claims, allowing an unauthenticated attacker to impersonate existing users, including administrators.
 Best Practices
Use this admin panel security checklist to review MFA, sessions, authorization, exposed routes, recovery access, logging, secure cookies, and operational controls.
 Best Practices
Learn how to manage API keys, environment variables, CI/CD secrets, service credentials, and frontend configuration without leaking sensitive values into repositories or public bundles.
 News
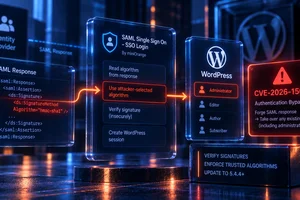
CVE-2026-15013 is a critical authentication bypass in the SAML Single Sign On - SSO Login plugin for WordPress through version 5.4.3. The plugin can be tricked into validating an attacker-controlled SAML response with the wrong signature algorithm, allowing unauthenticated attackers to impersonate existing users, including administrators.
 Best Practices
Learn how to secure web application file uploads with allowlists, content validation, isolated storage, safe filenames, resource limits, authorization, and practical testing.
 Platform Security
Learn what JavaScript source maps expose in production, when they become a security risk, how to audit deployed maps, and how to keep debugging useful without leaking unnecessary source context.
 News
CVE-2026-46579 is an OpenShift Router authentication flaw that can allow crafted X-SSL-Client-* headers sent over plain HTTP to reach a backend when insecureEdgeTerminationPolicy is set to Allow. Backends that trust those headers as proof of a client certificate can be tricked into accepting an attacker-controlled identity.
 Platform Security
Learn what server headers, framework markers, frontend metadata, error pages, and public assets reveal about a website, when disclosure matters, and what to fix first.