 News
Security Brief: Exploit in Joomla JCE Enables PHP Code Execution
A critical Joomla JCE flaw is being actively exploited to run unauthorized PHP code. Website owners using affected versions must act now to secure their sites.
Expert articles on web security, vulnerabilities, and best practices
NewsA critical Joomla JCE flaw is being actively exploited to run unauthorized PHP code. Website owners using affected versions must act now to secure their sites.
 News
Learn about CVE-2026-48902 affecting Joomla! CMS versions 3.9.0-5.4.5, 6.0.0-6.1.0, causing potential security issues with password reset links when HTTPS is not enforced.
 Product
A 2026 tour of Vulnify free tools: DNS and email playbooks, browser-only developer utilities, Permissions-Policy analysis, CAA checks, and WAF-aware scanning—plus where to start.
 Guides
Before launch day, run eight free Vulnify checks: vulnerability scan, headers, SSL, DNS, email auth, subdomain exposure, CAA, and blacklist status. A practical go-live checklist for site owners.
 Platform Security
Cloudflare, Akamai, and other edge layers change how scanners see your site. Learn what WAF and CDN detection tells you, when results differ from origin, and how to interpret Vulnify findings.
 Product
Decode JWT headers and payloads, verify HMAC signatures, and generate password hashes locally in your browser. Vulnify developer tools never upload tokens or secrets to our servers.
 Guides
Security headers protect transport and content execution; Permissions-Policy restricts browser features like camera and geolocation. Learn how they differ and when to test both on Vulnify.
 Guides
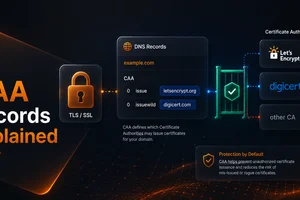
CAA records tell certificate authorities which CAs may issue TLS certificates for your domain. Learn what issue and issuewild mean, why missing CAA matters, and how to review policy with Vulnify.
 Guides
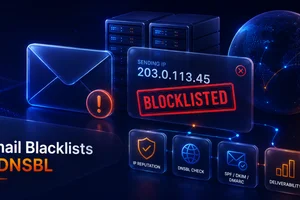
DNSBL listings can block mail and damage domain reputation overnight. Learn how public blacklists work, when to check them, and how to investigate listings with Vulnify free tools.
 Guides
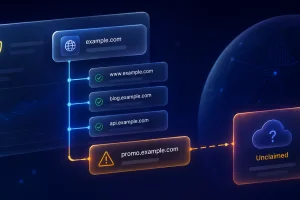
Subdomain takeover happens when DNS still points at a service you no longer control. Learn how attackers abuse dangling CNAMEs and how to find them before someone else claims your subdomain.